Securing ISO certification rapidly is not about hiring expensive consultants, but about implementing a lean, internally-led compliance strategy focused on winning UK government tenders.
- ISO 14001 (Environmental) is now a decisive factor for winning public contracts under the UK’s Procurement Act 2023.
- Digital-first documentation and risk-based supplier audits are key to eliminating administrative overload and preventing non-conformances.
Recommendation: Focus on training internal champions and implementing a unified data system to meet multiple compliance needs (ISO, SECR, UK ETS) simultaneously, turning compliance into a competitive advantage.
For Quality Assurance Managers and Managing Directors in UK manufacturing, the path to ISO certification can seem like a daunting maze of complex documentation, stringent audits, and significant financial investment. The pressure is amplified when lucrative public sector tenders—the lifeblood of many industrial businesses—are gated behind these very certifications. It’s a high-stakes environment where a non-conformance can mean more than a failed audit; it can mean a lost contract and a compromised growth trajectory.
The conventional wisdom often points towards one solution: hiring expensive external consultants to navigate the bureaucracy. This approach, while common, frequently leads to a dependency culture and a quality management system (QMS) that is poorly integrated with daily operations. Many businesses believe the administrative burden of documenting audit procedures and managing supplier compliance is an unavoidable cost of doing business. But what if this entire premise is flawed?
What if the most efficient, cost-effective, and strategically sound path to certification was not through outsourcing, but through empowerment? This procedural guide is built on a veteran auditor’s perspective: true compliance excellence comes from within. It’s about building a lean, resilient, and digitally-native system that not only satisfies the auditor but also drives genuine operational improvement and, crucially, positions your company to win.
This article will deconstruct the process, moving beyond the platitudes to provide a clear, procedural roadmap. We will dismantle the myth of consultant dependency, provide a framework for lean documentation, clarify which certifications hold the most weight for government contracts, and highlight the critical failure points that must be avoided. We will also provide clear guidance on aligning with new environmental reporting standards, a non-negotiable for any UK manufacturer with public sector ambitions.
The following sections provide a detailed breakdown of the key strategic areas you must master to achieve rapid and robust ISO certification. This is your procedural map to transforming a regulatory hurdle into a powerful engine for growth.
Contents: Your Roadmap to Rapid UK ISO Certification
- Why Believing ISO 9001 Requires Hiring Costly External Consultants Is False?
- How to Document Internal Audit Procedures Without Creating Admin Overload?
- ISO 9001 vs ISO 14001: Which Certification Wins More Government Tenders?
- The Document Control Failure That Guarantees an Immediate Non-Conformance
- Streamlining Your Supplier Evaluation Criteria to Meet Compliance Effortlessly
- SASB vs TCFD Frameworks: Which Aligns Best With British Regulatory Standards?
- The Double-Counting Data Flaw That Triggers Immediate HMRC Fines
- Tracking and Reducing Industrial Emissions for UK Regulatory Compliance
Why Believing ISO 9001 Requires Hiring Costly External Consultants Is False?
The most pervasive myth in the world of quality management is that achieving ISO 9001 certification requires a substantial budget for external consultants. This belief stems from the perceived complexity of the standard, but it overlooks a far more powerful and cost-effective alternative: the Internal Champion Model. This strategy involves identifying high-potential employees within your organisation and investing in their expertise through certified training. An employee with deep operational knowledge who understands the standard is infinitely more valuable than an external consultant who only sees a snapshot of your business.
The financial case is compelling. A typical consultant can charge £800-£1,200 per day, leading to project costs that easily spiral into tens of thousands. In contrast, while ISO 9001 certification can start from £995 for small businesses utilising streamlined approaches, the core investment should be in people. A 5-day CQI/IRCA certified Lead Auditor course from a reputable body like BSI costs around £1,495 + VAT—a one-time investment that builds a permanent internal asset. Furthermore, UK manufacturers can often leverage Made Smarter grants, which can cover up to 50% of these training costs, dramatically lowering the barrier to entry.
The success of this model is not theoretical. It’s proven in practice by numerous SMEs across the UK.
Case Study: Pace Engineering’s Self-Implementation Success
Pace Engineering’s two-person team successfully achieved ISO 9001 certification without any external consultants. By leveraging internal expertise and using structured toolkits, they demonstrated that small UK manufacturers can independently implement a robust quality management system. This approach not only saved significant costs but also ensured the resulting QMS was perfectly tailored to their specific operational realities, rather than being a generic template imposed by an outsider.
By empowering your own team, you are not just preparing for an audit; you are embedding a culture of quality that persists long after the certificate is on the wall. This internal ownership is the true hallmark of a world-class manufacturing operation.
How to Document Internal Audit Procedures Without Creating Admin Overload?
The second major fear holding manufacturers back from ISO certification is the spectre of documentation—endless binders, complex manuals, and a bureaucratic system that suffocates productivity. Traditional documentation is indeed a source of administrative overload. However, the modern approach, favoured by auditors who value effectiveness over volume, is Lean Documentation. This is not about having less documentation; it’s about having smarter, more effective documentation that serves a real purpose.
The core principle is to move from text-heavy manuals to visual, integrated systems. Instead of a 100-page quality manual that no one reads, a lean system uses visual process maps that clearly depict workflows. Instead of cumbersome paper-based audit records, it leverages live dashboards that pull data directly from your ERP or MES systems. This eliminates the risk of version control errors—a common source of non-conformance—by establishing a « single source of truth » for all procedures and records.
This shift from traditional to lean documentation has a transformative impact on audit preparation, turning a weeks-long scramble for evidence into a routine, data-driven process. The time savings are substantial and directly address the « admin overload » concern.
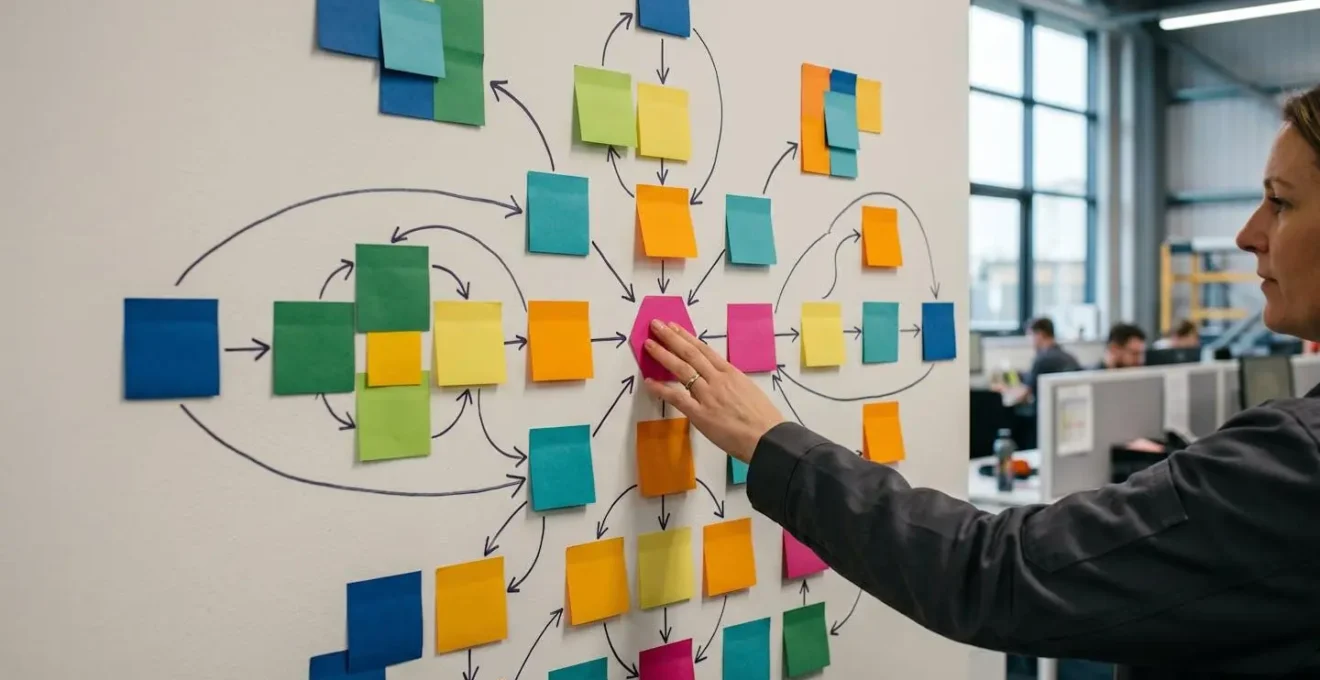
The table below, based on best practices promoted by UK business advisors, highlights the dramatic efficiency gains. Adopting these lean principles is not just about passing an audit; it’s about building a more agile, responsive, and efficient operation.
| Traditional Documentation | Lean Documentation | Time Savings |
|---|---|---|
| 100+ page quality manual | Visual process maps | 70% reduction in creation time |
| Separate audit records | Live dashboard metrics | Real-time data access |
| Multiple document versions | Single source of truth | Zero version control issues |
| Manual evidence collection | Automated ERP integration | 80% faster audit preparation |
ISO 9001 vs ISO 14001: Which Certification Wins More Government Tenders?
For years, ISO 9001 (Quality Management) was the default standard for accessing commercial opportunities. It remains foundational. However, for UK manufacturers targeting public sector work, the strategic landscape has fundamentally shifted. The decisive question is no longer just « Is your quality good? » but « Is your operation sustainable? ». Consequently, ISO 14001 (Environmental Management) has become the new kingmaker for winning government tenders.
This is not a trend; it is a regulatory mandate. The UK’s Procurement Act 2023 has hardwired environmental considerations into the public procurement process, affecting over £300 billion in annual spending. The legislation explicitly empowers public bodies to favour suppliers who can demonstrate robust environmental management. An ISO 14001 certification is the most universally recognised and credible way to provide this assurance. It moves environmental performance from a vague corporate statement to a verifiable, audited fact.
Analysis of recent procurement law changes shows that with ISO 14001 certification now essential for UK public contracts, organisations without it are at a significant competitive disadvantage. The Crown Commercial Service (CCS), which manages procurement for the central government, reinforces this point by making a supplier’s Carbon Reduction Plan (CRP) a prerequisite for major tenders.
Case Study: Crown Commercial Service Environmental Requirements
Under PPN 06/21, the Crown Commercial Service (CCS) now mandates that suppliers bidding for major government contracts must have a Carbon Reduction Plan in place. This policy covers over £300 billion of public procurement. ISO 14001 provides the perfect, internationally recognised framework for developing, implementing, and verifying such a plan. UK manufacturers with ISO 14001 are therefore pre-qualified for these requirements, while their competitors are left scrambling to create and validate a plan from scratch, demonstrating the standard’s direct link to winning central government contracts.
The conclusion is clear for any UK manufacturer with public sector ambitions: while ISO 9001 is the ticket to the game, ISO 14001 is increasingly the key to winning it. Pursuing them in parallel is the most strategically astute approach.
The Document Control Failure That Guarantees an Immediate Non-Conformance
In the procedural world of ISO audits, there are minor issues, and then there are « showstoppers. » The single most common and guaranteed way to receive an immediate major non-conformance is a failure in document control, specifically, an employee being found working from an obsolete or uncontrolled document. This isn’t just a procedural slip-up; to an auditor, it signals a fundamental breakdown of the entire quality management system. If you cannot control your own instructions, how can you possibly control the quality of your product?
This failure often happens with the best of intentions. An experienced operator laminates a work instruction for durability, unaware that the process has since been updated. A supervisor prints a procedure to take to the factory floor, creating an uncontrolled copy that quickly becomes outdated. These seemingly innocuous actions can have catastrophic audit consequences. The only acceptable solution is a system that makes it impossible to use an outdated document.
Modern, digital-first document control is the answer. This involves moving away from physical paper on the shop floor and embracing a single, centrally controlled digital repository. The goal is to ensure that the only version of a document a user can ever access is the current, approved version. This requires a robust system, but the principles are straightforward and can be implemented with existing technology.
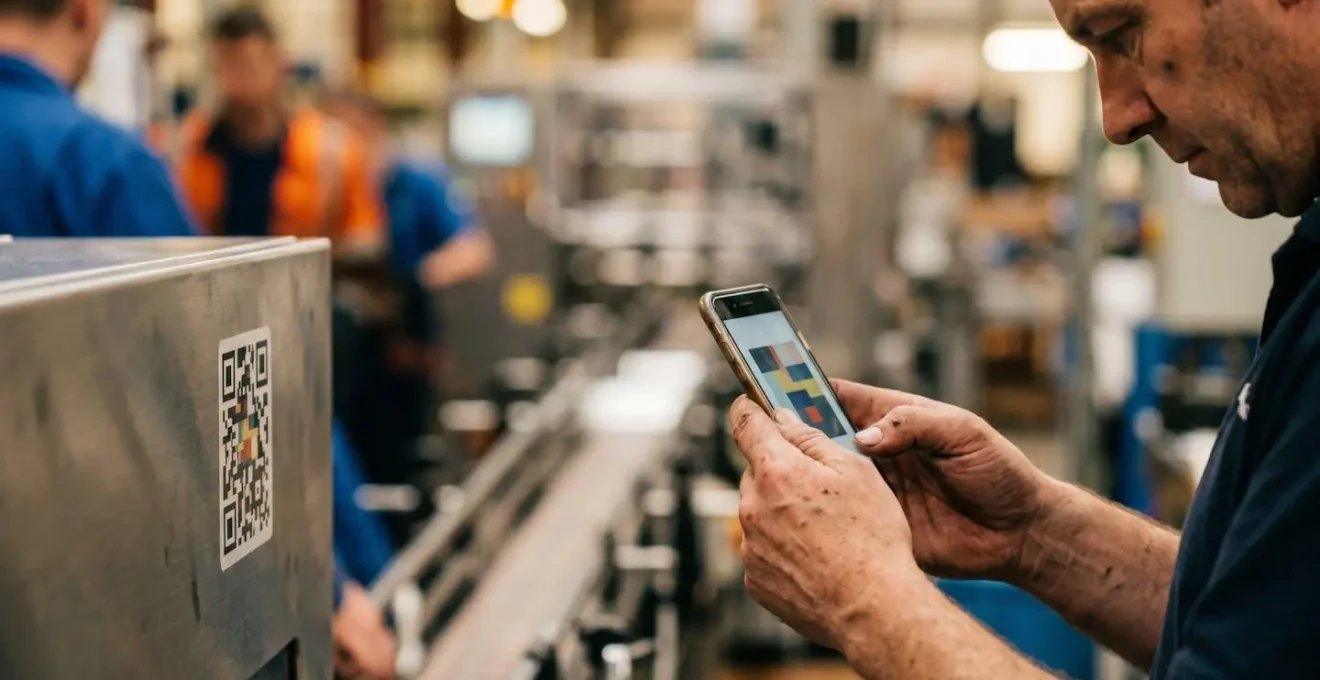
Action Plan: Critical Document Control Checkpoints
- QR Code Implementation: Systematically remove all paper and laminated work instructions from the factory floor. Replace them with durable QR codes placed directly on machinery, which link to the controlled digital document in your central system.
- Training Record Alignment: Configure your system so that every update to a procedure automatically triggers a training requirement for affected staff. The training record, dated within 30 days of the update, becomes the objective evidence that the change has been communicated.
- Digital Policy Enforcement: Set network drive and document management system permissions to « read-only » for the vast majority of users. Prevent local saving, printing, or copying of controlled documents to eliminate the creation of uncontrolled copies.
- Version Control Audit Trail: Ensure your system maintains an automated, tamper-proof log. The log must show who accessed which document version, and when, providing a clear audit trail for the auditor.
- Obsolete Document Quarantine: Establish an automated workflow where, upon approval of a new version, the superseded document is immediately and automatically moved to a secure, restricted-access « archive » folder. This prevents any possibility of it being used accidentally.
By implementing these checkpoints, you don’t just prevent a non-conformance; you build a resilient, error-proof system that auditors are trained to recognise as a sign of compliance maturity.
Streamlining Your Supplier Evaluation Criteria to Meet Compliance Effortlessly
A compliant internal system is only half the battle. Your ISO certification is only as strong as the weakest link in your supply chain. Both ISO 9001 and ISO 14001 require you to have a robust process for evaluating and controlling your suppliers. However, this does not mean you must subject your supplier of office stationery to the same level of scrutiny as the provider of your critical raw materials. A risk-based supplier tiering system is the key to meeting this requirement effortlessly and without creating unnecessary administrative work.
This approach involves categorising your suppliers into tiers—typically Critical, Medium, and Low—based on the impact their failure would have on your product, service, or compliance status. Each tier is then assigned a proportionate level of evaluation and monitoring. This ensures your resources are focused where the risk is highest, a methodology that auditors view very favourably as it demonstrates a mature understanding of risk management.
Furthermore, this evaluation process is not just an ISO exercise. It must be integrated with other legal requirements. In the UK, a critical example is the Modern Slavery Act 2015. With 547 UK government contracts now requiring Modern Slavery Act compliance verification, integrating this check into your supplier onboarding is no longer optional. A tiered system provides the perfect framework to do this efficiently.
A well-structured tiering system, like the example below, provides a clear, defensible logic for your supplier management activities, making the audit process smooth and predictable.
| Supplier Risk Level | Evaluation Method | Frequency | Documentation Required |
|---|---|---|---|
| Critical (Production materials) | Full on-site audit | Annual | ISO 9001 cert + Modern Slavery statement |
| Medium (Support services) | Remote audit | Bi-annual | Self-assessment + Insurance certificates |
| Low (Office supplies) | Digital questionnaire | Every 3 years | Basic company registration only |
By adopting this streamlined, risk-based approach, you transform supplier compliance from a bureaucratic checklist into a strategic function that protects your business and satisfies your auditor.
SASB vs TCFD Frameworks: Which Aligns Best With British Regulatory Standards?
As environmental reporting moves from a voluntary act to a legal obligation, UK manufacturers face a confusing « alphabet soup » of reporting frameworks. Two of the most prominent are SASB (Sustainability Accounting Standards Board) and TCFD (Task Force on Climate-related Financial Disclosures). While both aim to improve transparency, they serve different purposes, and for UK companies, one is non-negotiable.
The choice is not a matter of preference but of legal compliance. As the UK government has explicitly stated, TCFD-aligned reporting is now a legal requirement for many large UK firms under the Companies Act 2006. This makes TCFD the mandatory baseline. Its focus is on governance, strategy, risk management, and metrics related to climate change, aligning perfectly with the data required for Streamlined Energy and Carbon Reporting (SECR).
TCFD-aligned reporting is now a legal requirement for many UK firms under the Companies Act 2006, making it the non-negotiable baseline.
– UK Government, Companies Act 2006 Amendment
SASB, on the other hand, is currently a voluntary enhancement in the UK. Its strength lies in providing industry-specific metrics that allow for direct comparison between companies in the same sector. While not mandatory today, adopting SASB standards is a strategically wise move. It prepares a company for the forthcoming UK Sustainability Disclosure Requirements (SDR), which are expected to integrate SASB’s industry-specific approach. Therefore, the optimal strategy is not to choose between TCFD and SASB, but to use them together. TCFD meets your legal obligation, while SASB provides the detailed, industry-relevant data that demonstrates leadership and future-proofs your reporting.
This combined approach allows a manufacturer to use the same underlying data to satisfy multiple reporting needs, embodying the « collect once, use many times » principle that is central to efficient compliance.
The Double-Counting Data Flaw That Triggers Immediate HMRC Fines
In the high-stakes world of emissions reporting, data integrity is paramount. For UK manufacturers participating in schemes like the UK Emissions Trading Scheme (UK ETS), a simple data management error can lead to a devastating financial penalty. The most dangerous and surprisingly common of these errors is double-counting: reporting the same emission under two different categories or from two different sites within the same corporate group. This flaw doesn’t just invalidate your data; it can be interpreted by HMRC as an attempt to misrepresent your emissions footprint, triggering immediate and severe fines.
Double-counting typically occurs when different departments or sites use separate, un-reconciled spreadsheets to track emissions. A classic example is when Scope 2 electricity usage is calculated using both location-based and market-based methods without a clear reconciliation, or when a sub-component with an embedded carbon footprint is transferred between two UK sites and its emissions are counted at both locations. With over £300 billion of UK public procurement now covered by carbon reporting requirements, the pressure for accurate, auditable data has never been higher.
The only watertight solution is to establish a Single Emissions Source Registry. This is a centralised database that acts as the single source of truth for every emission-producing asset or activity in your organisation. Before any data is entered into your reporting for UK ETS, SECR, or ISO 14001, it must be validated against this master registry. This registry is not just a list; it’s a control system with strict validation rules designed to make double-counting a technical impossibility.
Implementing such a registry requires a disciplined, procedural approach to ensure every emission source is uniquely identified and tracked, preventing the costly errors that arise from siloed data.
Key Takeaways
- Internal Expertise Over Consultants: The fastest and most cost-effective path to ISO certification is by training internal champions, not relying on expensive external consultants.
- ISO 14001 is Key for Tenders: For UK manufacturers, ISO 14001 (Environmental) is now more critical than ever for winning government contracts due to the Procurement Act 2023.
- Digital & Lean is Non-Negotiable: Eliminate admin overload and audit failures by adopting lean, digital-first systems for document control and supplier evaluation.
Tracking and Reducing Industrial Emissions for UK Regulatory Compliance
Successfully navigating the UK’s complex web of environmental regulations—from ISO 14001 to SECR, ESOS, and the UK ETS—hinges on a single, foundational capability: a unified data collection strategy. The era of managing compliance with disparate spreadsheets is over. A modern, compliant manufacturing operation requires a centralised system where emissions data is collected once and then leveraged across multiple reporting frameworks. This is the essence of turning a regulatory burden into a strategic asset.
This unified approach delivers immense efficiency gains. As one UK manufacturer discovered, implementing a central data system that served ISO 14001, SECR, ESOS, and UK ETS requirements simultaneously led to a 60% reduction in reporting time. More importantly, having an ISO 14001-verified emissions data system provides the credibility needed to unlock preferential green financing rates from major UK banks, directly linking good compliance with improved financial performance.
Building this unified system involves creating a UK-centric emissions tech stack. This means combining real-time data from on-site IoT sensors (for Scope 1), direct feeds from smart meters (for Scope 2), and structured data from supplier engagement platforms (for Scope 3). The goal is to automate data collection as much as possible, ensuring the information is accurate, timely, and, above all, auditable.
Ultimately, achieving excellence in emissions tracking is not an IT project; it is a core business process. It is the final, essential piece of the puzzle for UK manufacturers who wish to demonstrate leadership, de-risk their operations from regulatory penalties, and position themselves as the preferred supplier for a public sector that values sustainability as much as quality.
The next logical step for your organisation is to conduct a thorough internal gap analysis against these procedural frameworks. By identifying where your current systems fall short, you can create a targeted action plan for rapid, efficient, and successful ISO certification, positioning your company to win the contracts that will define its future.